


nis2
Compliance with NIS2 becomes straightforward, structured and under control.
The NIS2 Directive imposes new obligations regarding security, governance, risk management and incident reporting on companies and organisations operating in critical and digital sectors. Our platform helps you centralise activities, records and processes so that you can approach compliance in a structured manner.
What is the NIS2 Directive?
Does your company fall within the scope of NIS2?
The legislation applies to a wide range of public and private organisations, in particular medium-sized and large enterprises operating in critical or digital sectors.
Key topics
- Energy
- Transport
- Healthcare
- Banking and finance
- Digital infrastructure
- Telecommunications
Key figures
- Industry and manufacturing
- Food
- Chemicals
- Logistics and distribution
- Digital services and online platforms
MAKE IT YOURS
Company size is also a factor: medium-sized and large enterprises are normally included, but in some cases smaller organisations may also be included.
NIS2 requirements and risks for businesses
Conformità NIS2
Per adeguarsi alla NIS2 le aziende devono:
Registrarsi presso ACN ed essere incluse nel perimetro NIS
Designare un punto di contatto e referente CSIRT
Notificare gli incidenti significativi entro tempistiche definite
Implementare misure tecniche e organizzative adeguate
Gestire e documentare il rischio cyber
Garantire la supervisione diretta del management
I rischi della non conformità
Non adeguarsi alla NIS2 espone l’azienda a:
Sanzioni fino a 10 milioni di euro o 2% del fatturato globale per soggetti essenziali
Sanzioni fino a 7 milioni o 1,4% del fatturato globale per soggetti importanti
Responsabilità dirette del management
Possibili sospensioni e impatti operativi
NIS2 Compliance
To comply with NIS2, companies must:
Register with ACN and be included within the NIS scope
Appoint a point of contact and a CSIRT representative
Report significant incidents within the required timeframes
Implement appropriate technical and organizational measures
Manage and document cybersecurity risks
Ensure direct management oversight
The Risks of Non-Compliance
Failure to comply with NIS2 exposes companies to:
Fines of up to €10 million or 2% of global annual turnover for essential entities
Fines of up to €7 million or 1.4% of global annual turnover for important entities
Direct management accountability
Potential suspensions and operational disruptions
NIS2 compliance is not a one-off task: it requires ongoing updates, constant monitoring and the ability to respond to incidents. Delaying it means increasing the risk.
Nova by Cycorehub: the NIS2 compliance platform
Enterprise-grade cybersecurity.
Without enterprise complexity.
NOVA simplifies your company’s cyber security. A platform that combines SIEM and SOAR into a single, intuitive dashboard, to protect you, save you time and simplify compliance with ISO 27001 and NIS2.
Anteprima della dashboard NOVA - Tutto sotto controllo in un colpo d'occhio
Centralised dashboard
- Real-time security status across the entire network
- Visual map of devices with health indicators
- Timeline of events with automatic prioritisation
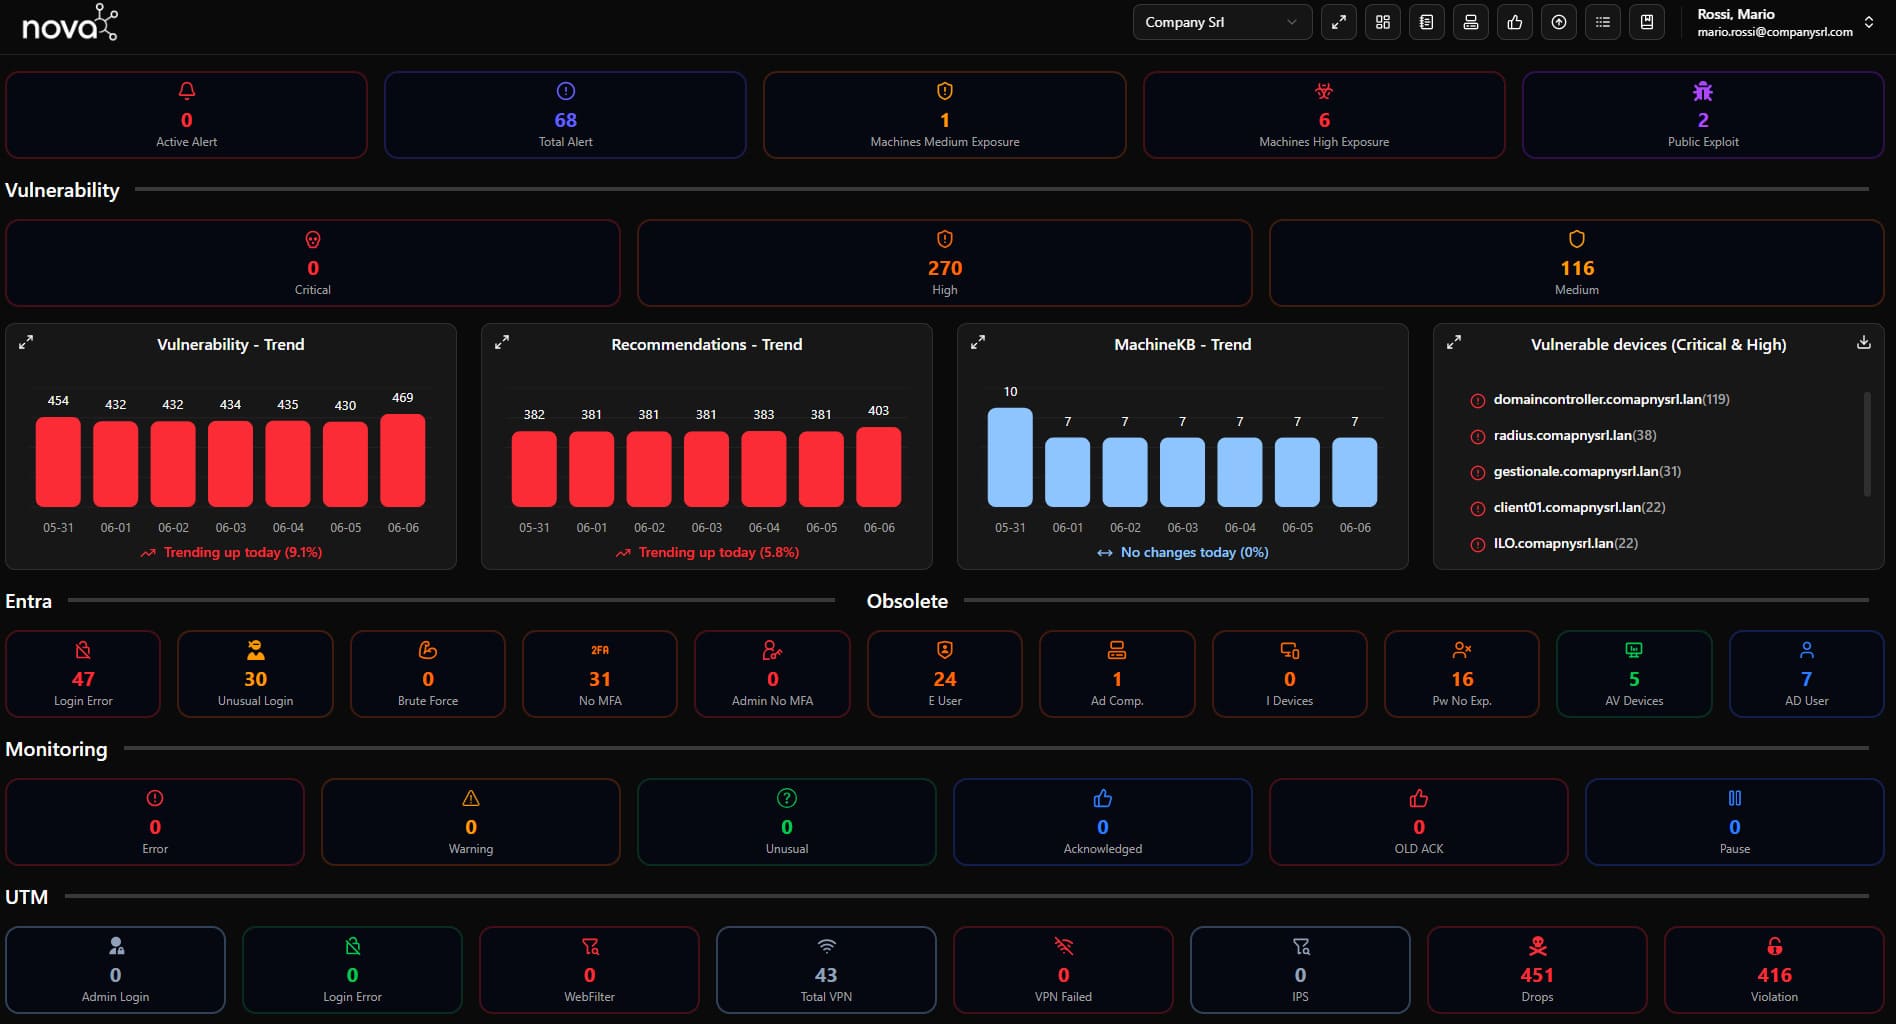
Tangible benefit
From 7 different interfaces to a single dashboard. Save 2 hours a day by eliminating the constant switching between tools.
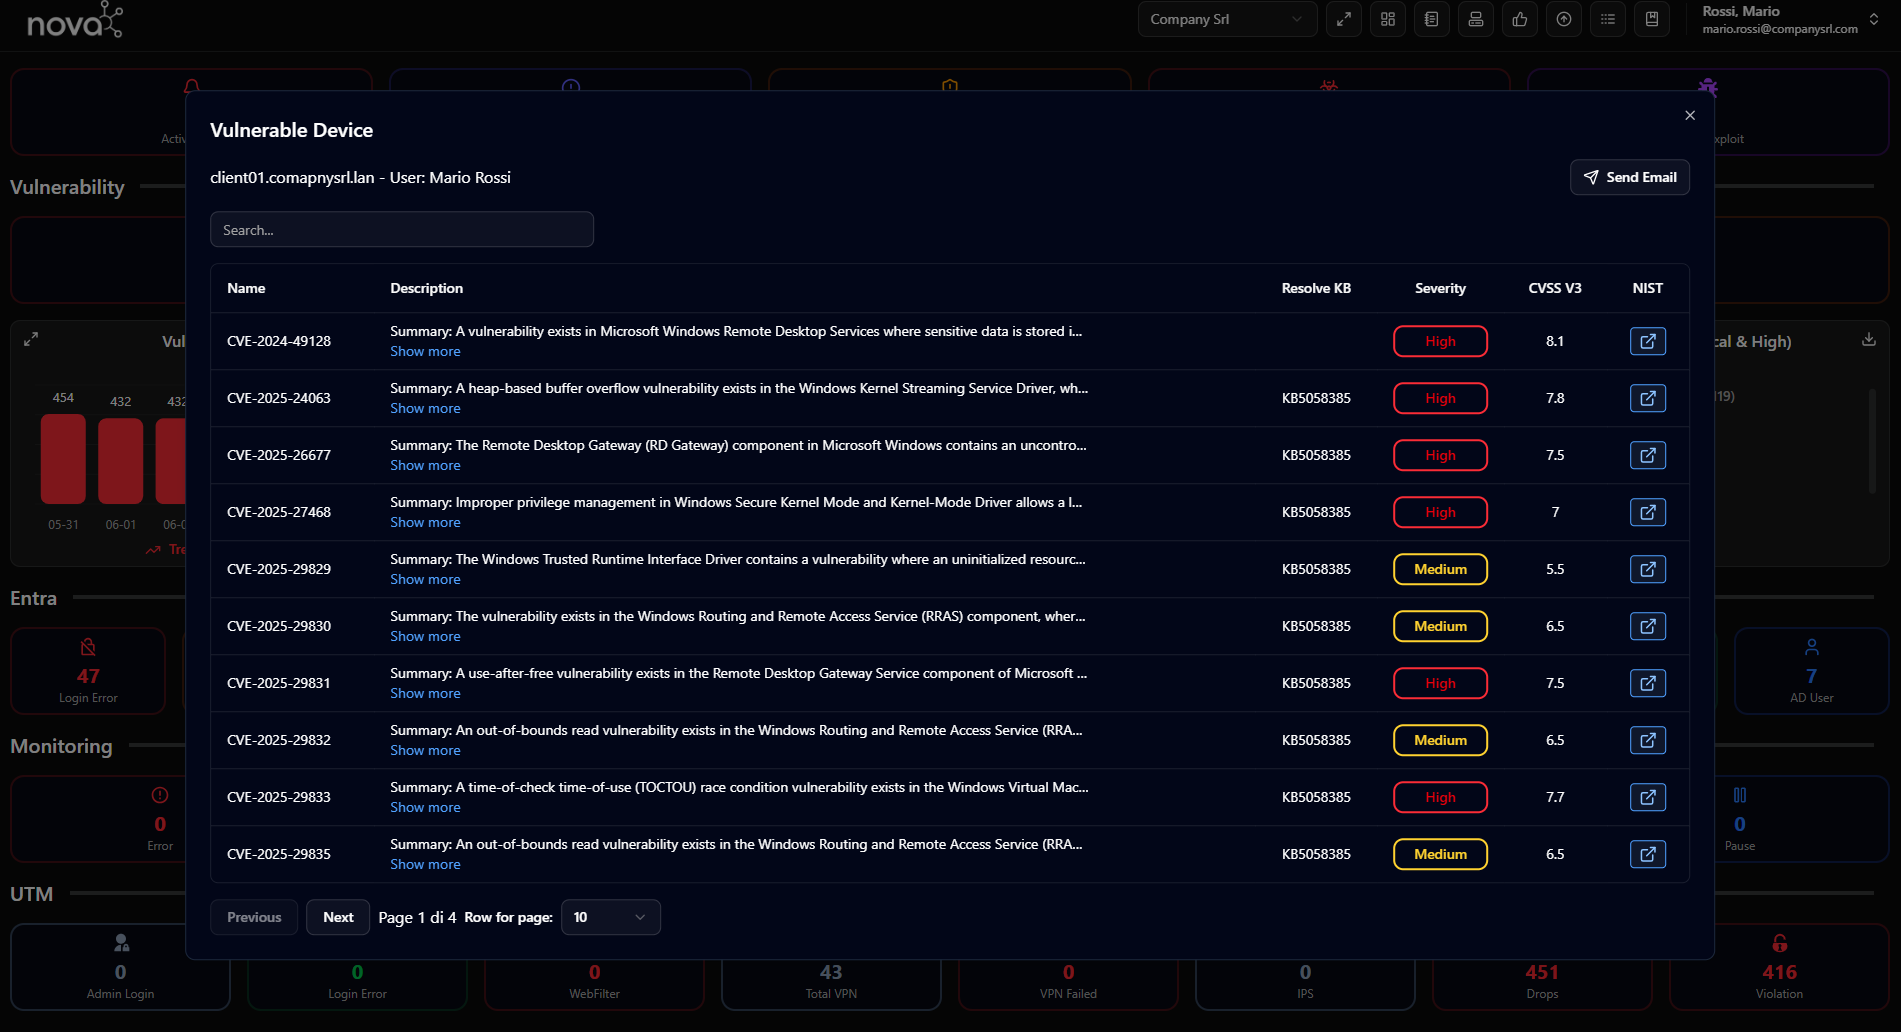
Smart alerts
- Machine learning that learns from your browsing patterns
- Automatic correlation of events to reduce false positives
- Prioritisation by business impact – critical threats highlighted
- Push notifications on your phone
Tangible benefit
Reducing false positives. Your phone only rings when it really needs to, so you can sleep soundly.
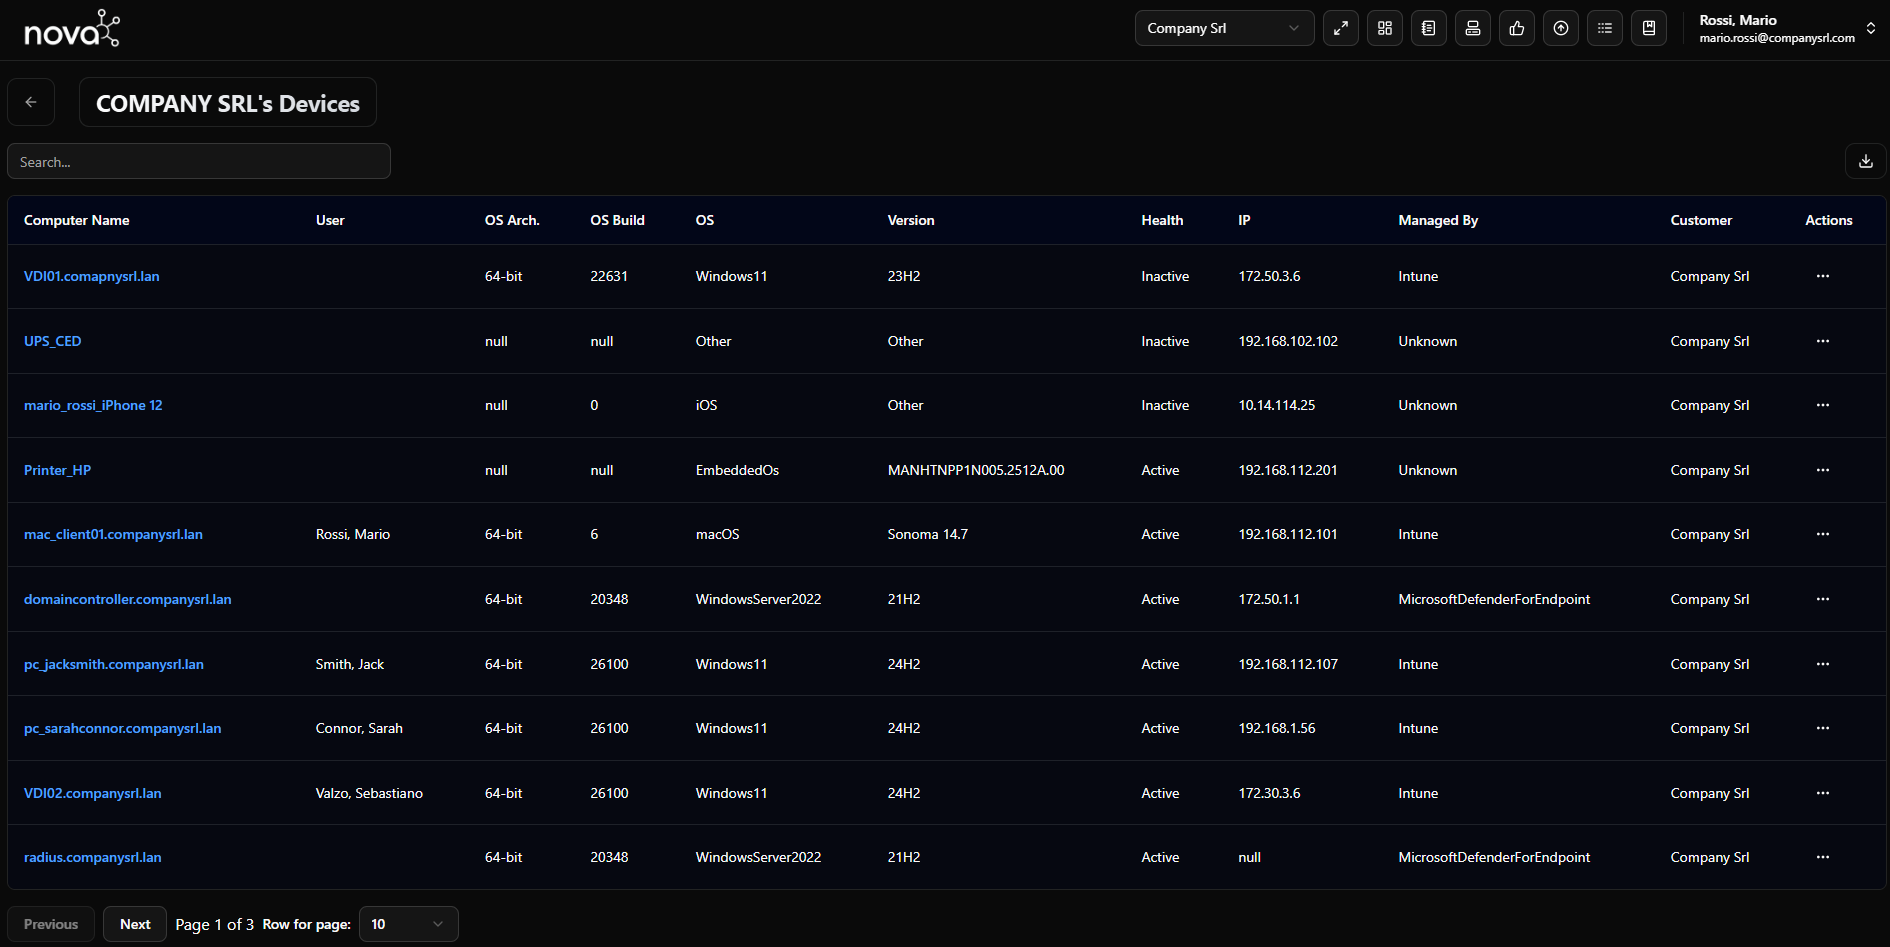
Immediate action
- Isolate an infected PC with a single click
- Run targeted scans on suspicious devices
- Block compromised users directly from Entra ID
Tangible benefit
From hours of manual intervention to minutes of automated action. Contain incidents before they spread
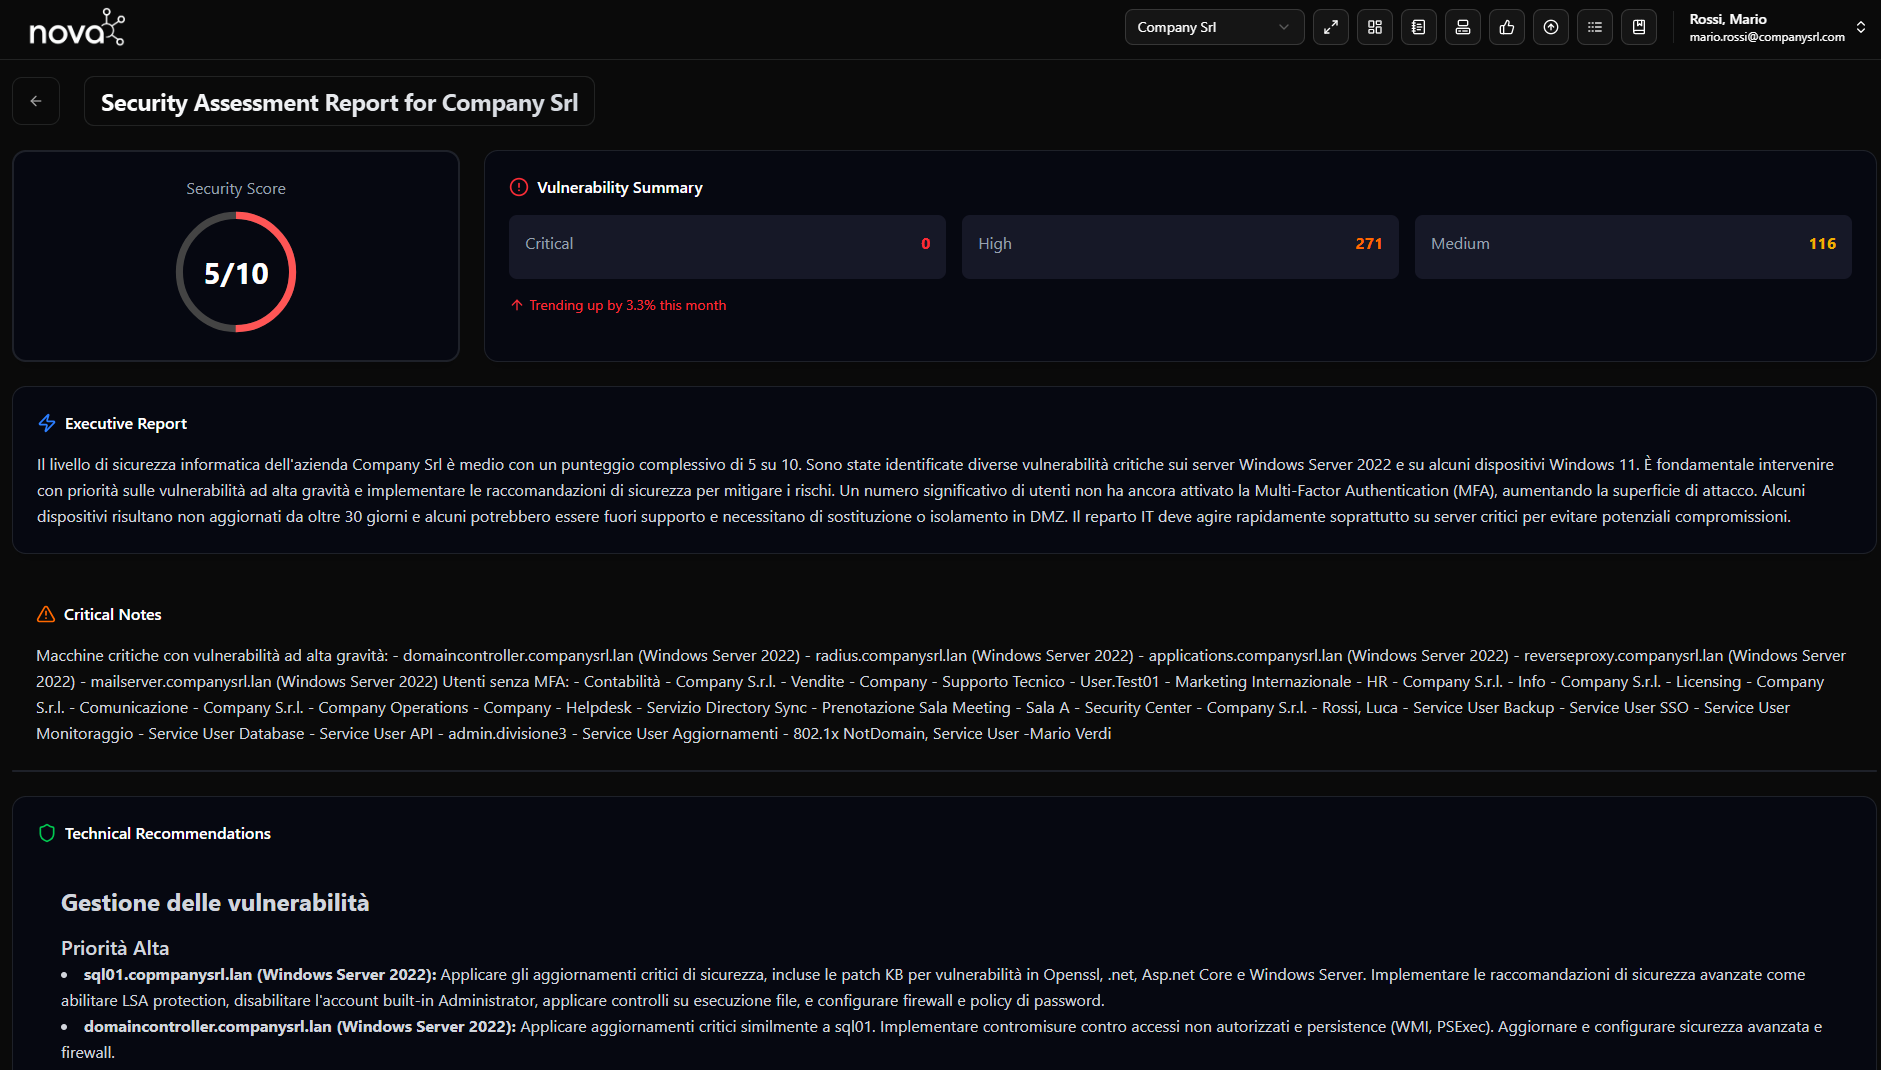
Automatic reports using AI
- Check list di compliance per GDPR, ISO 27001, AGID
- Executive summaries for management with clear KPIs
- Predictive analyses on vulnerabilities and risk trends
- Documents for audits and certifications
Tangible benefit
From monthly manual reports to automatic daily reports. AI writes the documents; you focus on strategy.
Native integrations
- Microsoft Defender for Business – comprehensive endpoint monitoring
- Fortinet Firewall – traffic control and VPN
- PRTG Network Monitor
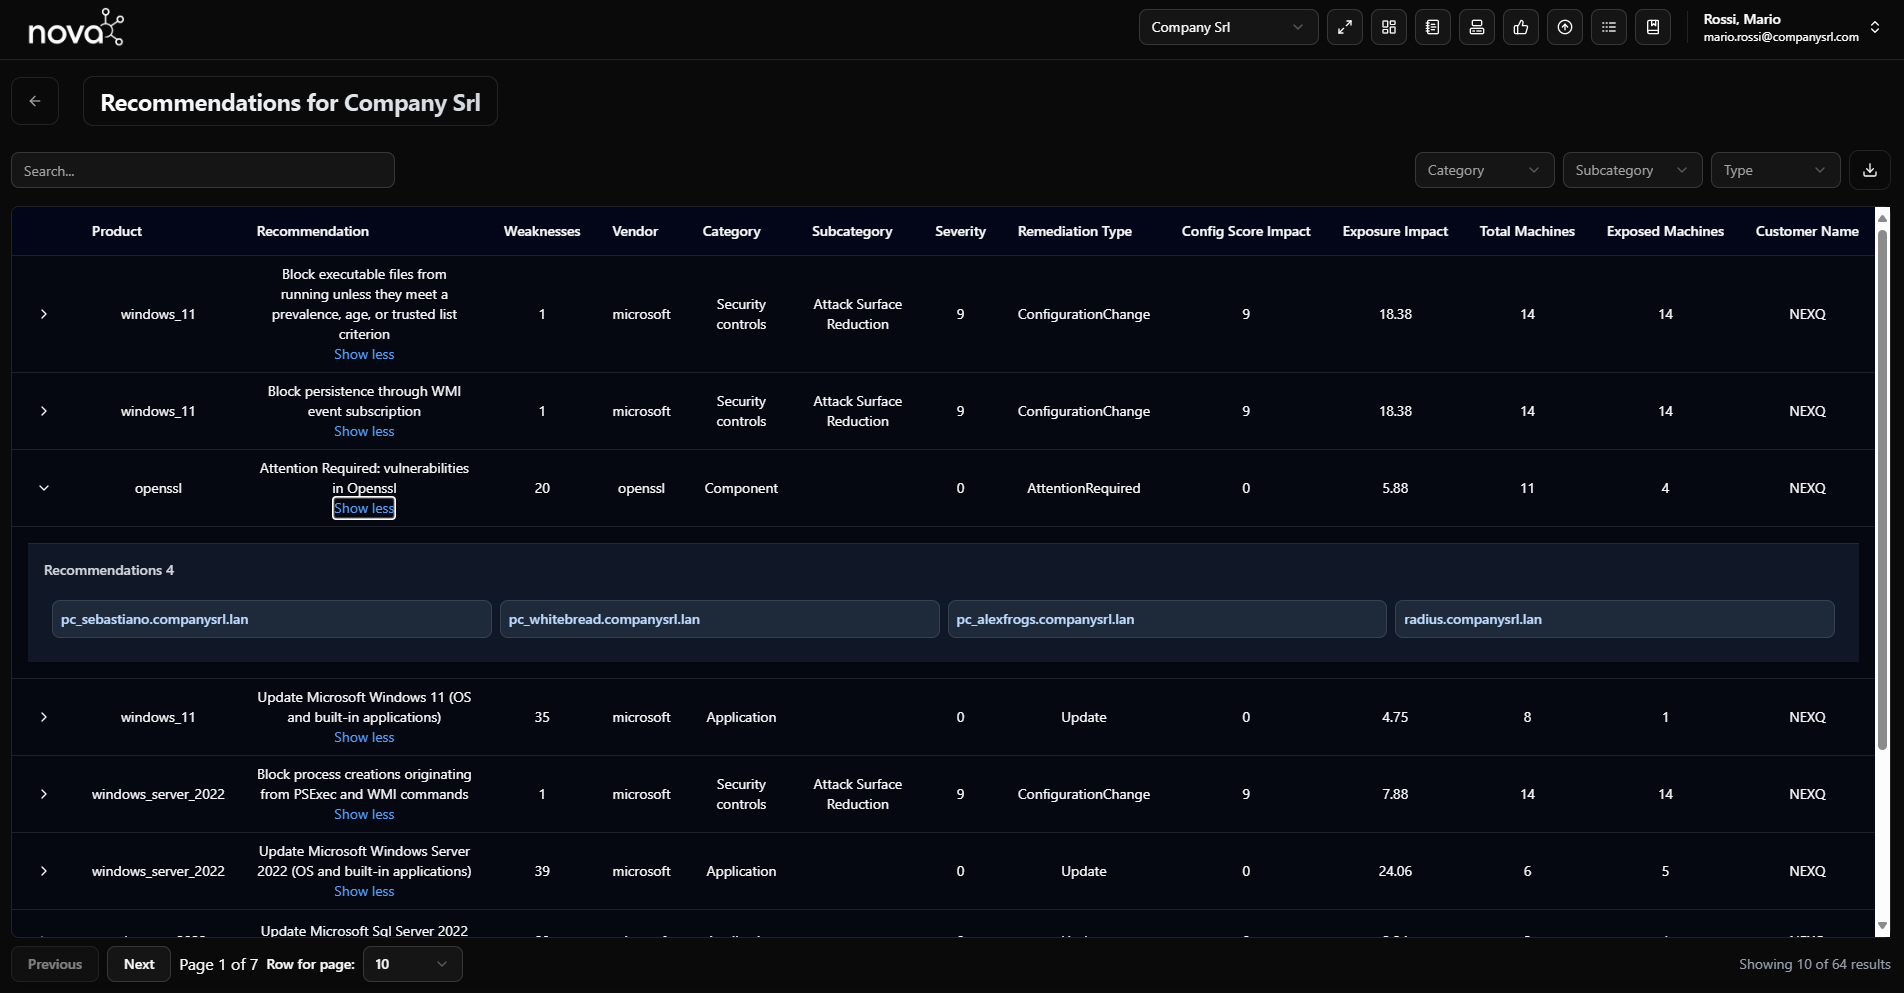
Tangible benefit
Set up in 3 days instead of 3 months. Integrations work straight out of the box, with no custom development*. You’ll have a solid foundation to ensure security, resilience and operational simplicity.
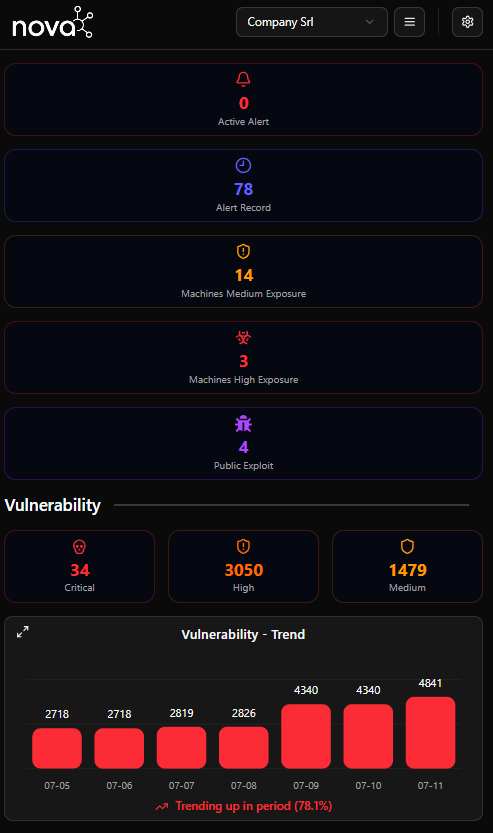
La cybersecurity enterprise.
Senza la complessità enterprise.
NOVA semplifica la sicurezza informatica della tua azienda. Una piattaforma che riunisce SIEM e SOAR in un’unica dashboard intuitiva, per proteggerti, farti risparmiare tempo e semplificare la conformità alle norme ISO 27001 e NIS2.
Anteprima della dashboard NOVA - Tutto sotto controllo in un colpo d'occhio
Dashboard centralizzata
- Stato di sicurezza in tempo reale di tutta la rete
- Mappa visuale dei dispositivi con indicatori di salute
- Timeline degli eventi con priorità automatica
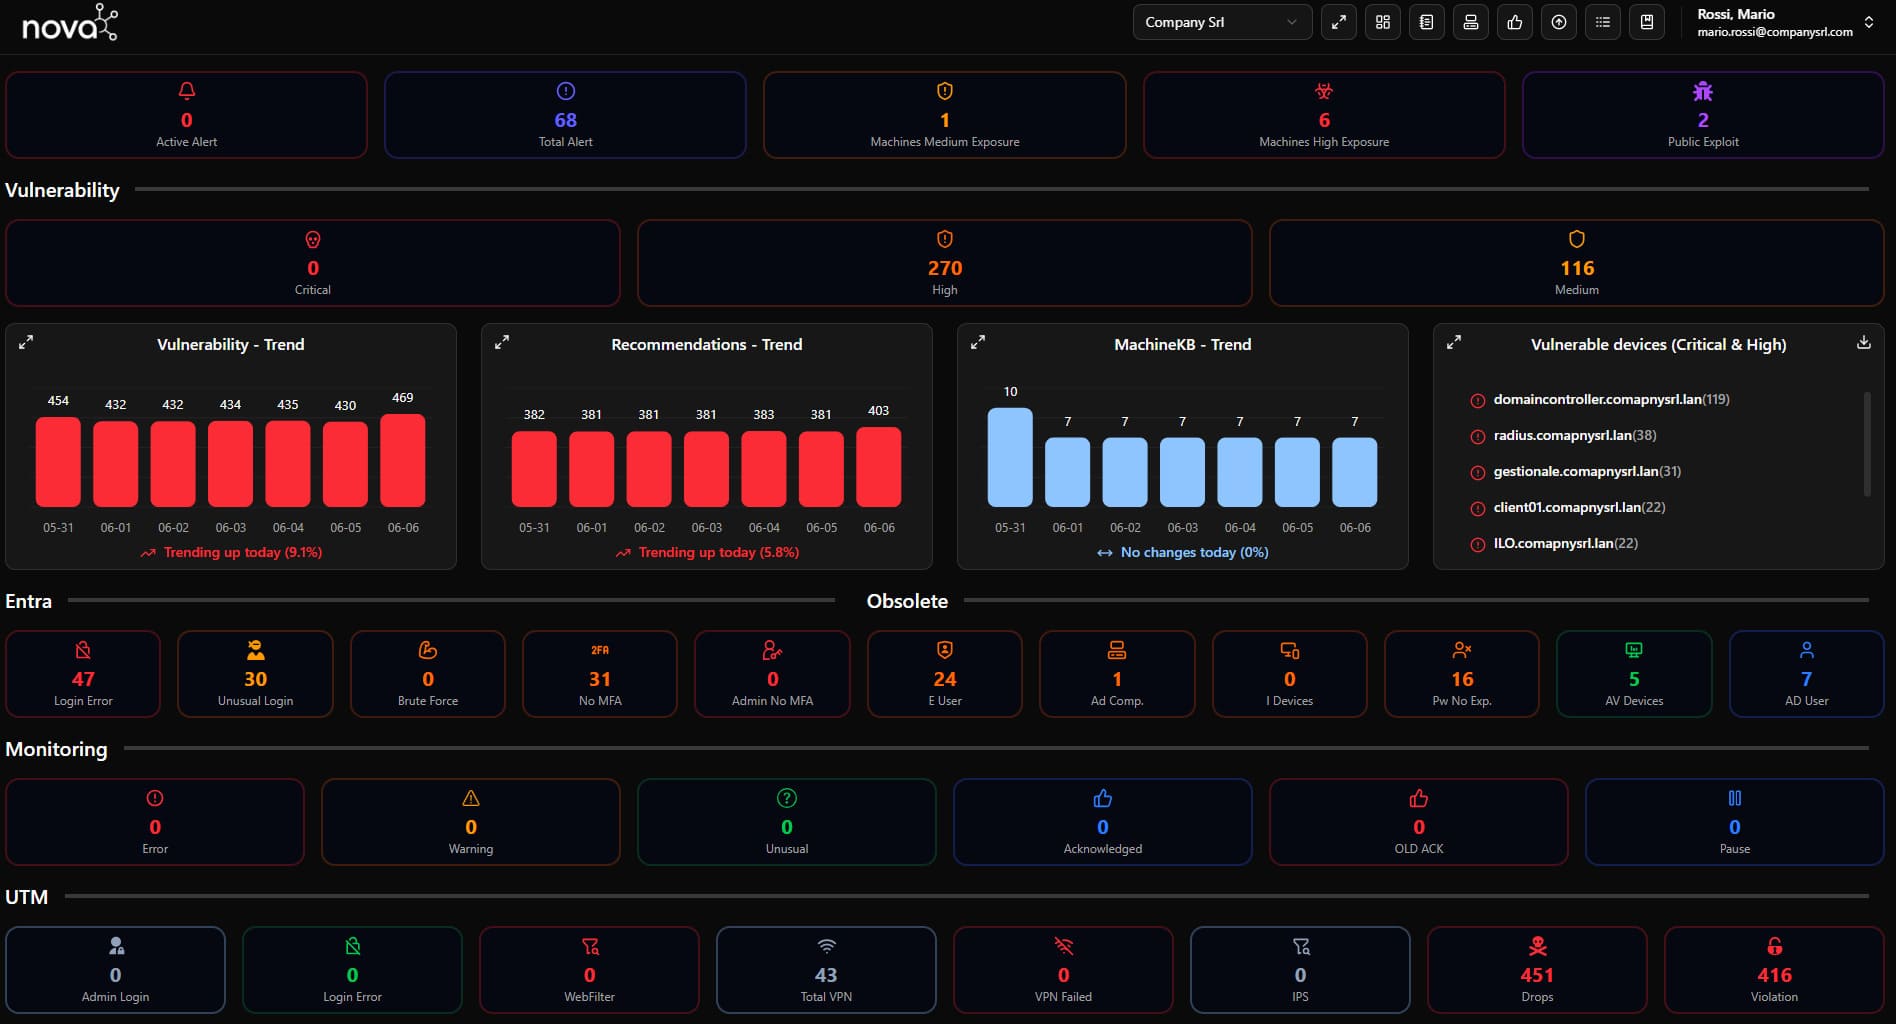
Beneficio concreto
Da 7 interfacce diverse a una sola dashboard. Risparmi 2 ore al giorno eliminando il salto continuo tra strumenti.
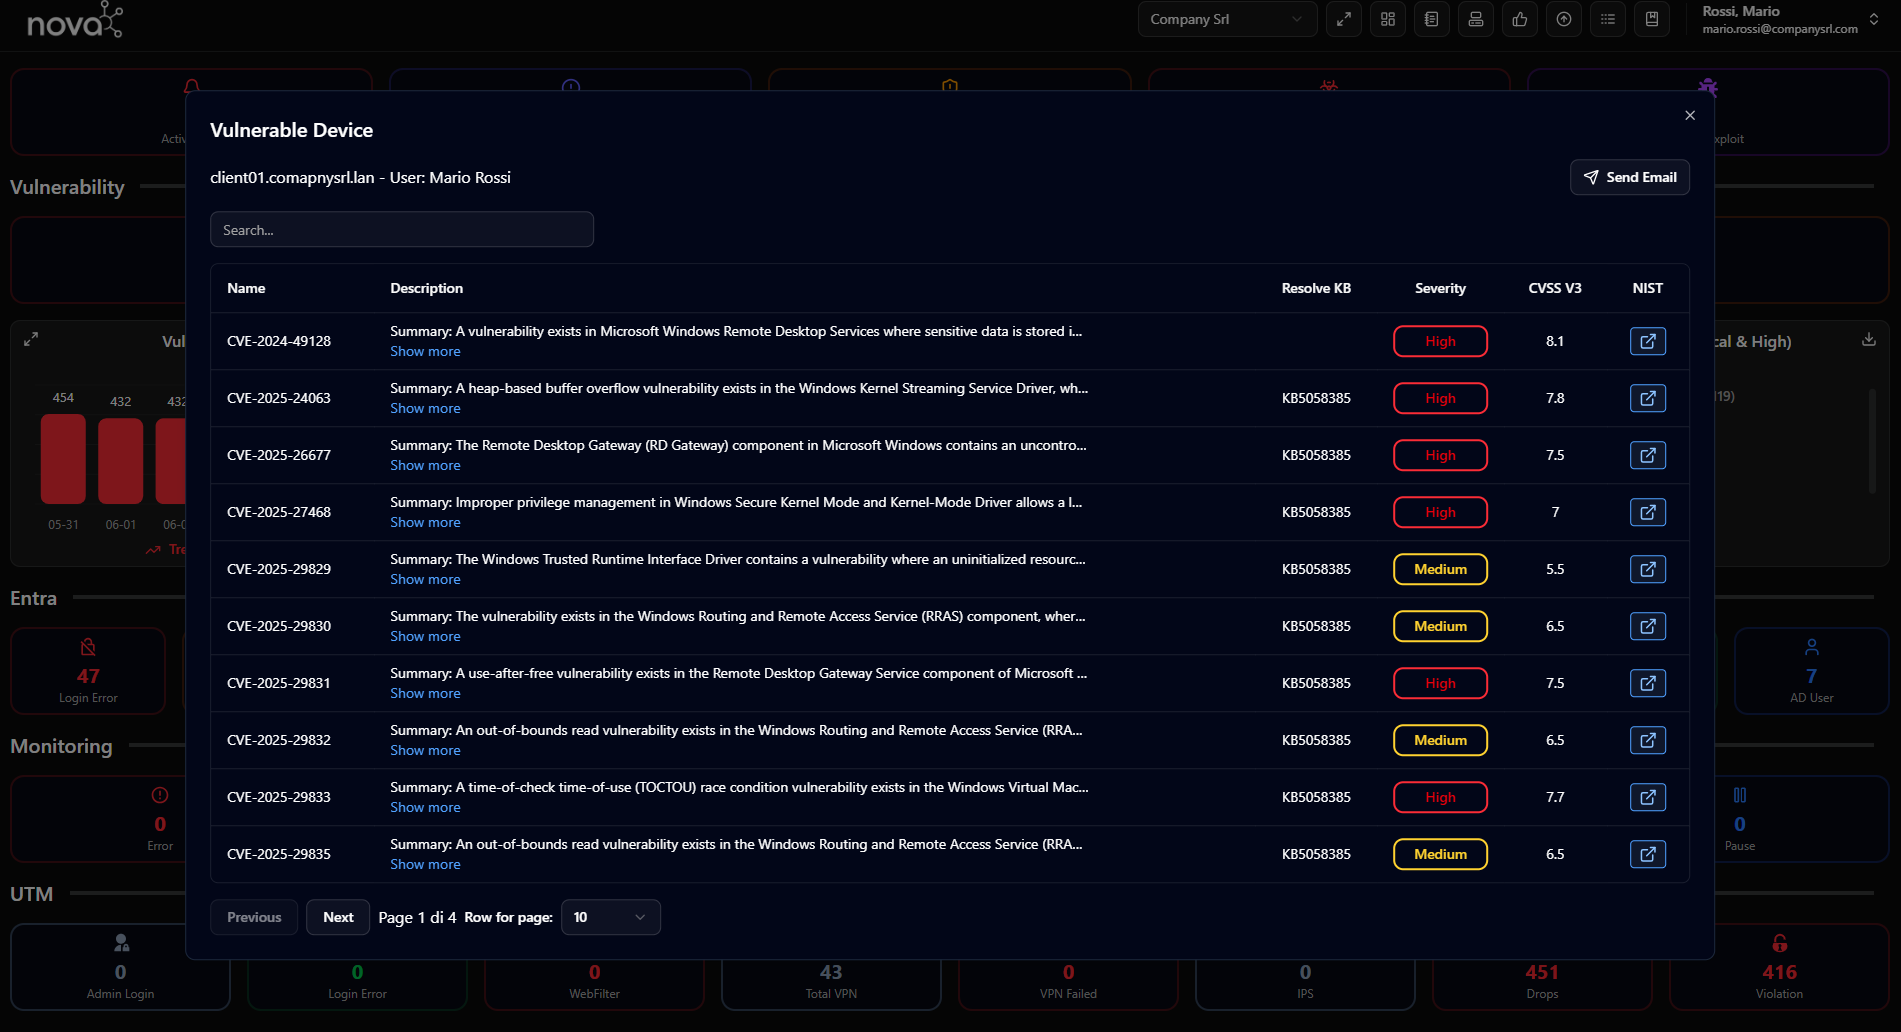
Alert intelligenti
- Machine learning che impara dai tuoi pattern di rete
- Correlazione automatica degli eventi per ridurre i falsi positivi
- Prioritizzazione per impatto business - le minacce critiche in evidenza
- Notifiche push sul telefono
Beneficio concreto
Riduzione falsi positivi. Il tuo telefono suona solo quando serve davvero, e puoi dormire tranquillo.
Azioni immediate
- Isolare un PC infetto con un clic
- Avviare scansioni mirate su dispositivi sospetti
- Bloccare utenti compromessi direttamente da Entra ID
Beneficio concreto
Da ore di intervento manuale a minuti di azione automatica. Contieni gli incidenti prima che si propaghino
Report automatici con AI
- Check list di compliance per GDPR, ISO 27001, AGID
- Summary esecutivi per il management con KPI chiari
- Analisi predittive su vulnerabilità e trend di rischio
- Documenti per audit e certificazioni
Beneficio concreto
Dal report manuale mensile al report automatico quotidiano. L'AI scrive i documenti, tu ti concentri sulla strategia.
Integrazioni native
- Microsoft Defender for Business - monitoring endpoint completo
- Firewall Fortinet - controllo traffico e VPN
- PRTG Network Monitor
Queste tre tecnologie rappresentano una combinazione ideale per le esigenze della Piccola e Media Impresa: protezione perimetrale, sicurezza degli endpoint e monitoraggio continuo dell’infrastruttura.
Queste tre tecnologie rappresentano una combinazione ideale per le esigenze della Piccola e Media Impresa: protezione perimetrale, sicurezza degli endpoint e monitoraggio continuo dell’infrastruttura.
Beneficio concreto
Setup in 3 giorni invece di 3 mesi. Le integrazioni funzionano out-of-the-box, senza sviluppi custom*. Avrai una base solida per garantire sicurezza, resilienza e semplicità operativa.
FAQ
The directive applies primarily to medium-sized and large enterprises operating in critical or digital sectors, but may also cover other organisations depending on the level of risk.
Generally speaking, micro-enterprises and small businesses are excluded, but they may be included in specific cases where the service provided is of critical importance.
Fines can be as high as 10 million euros or 2 per cent of annual global turnover for essential businesses.
All incidents that have, or may have, a significant impact on services must be reported within specific timeframes (24 hours, 72 hours, final report).
No. NIS2 also requires governance, processes, documentation and management accountability.
Nova supports the compliance process, helping to manage processes, controls and records in a structured and ongoing manner.
It depends on the organisation’s initial level of maturity, but it is essential to start as soon as possible in order to meet the deadlines set.
Centralise your cybersecurity management, reduce regulatory complexity and tackle compliance with greater control and visibility.